Security and privacy
Health data is among the most sensitive there is. In CuraDomus its protection is not an add-on: it is the very way the platform decides who sees what, keeps track of what happens and stores information.
The patient decides, every activity is tracked
The health record belongs to the patient. Through their consent, patients choose which information to share with professionals and family members, and can hide individual records at any time. Whoever wrote a record keeps seeing what they collected; everyone else sees only what has been shared with them.
Tailored permissions
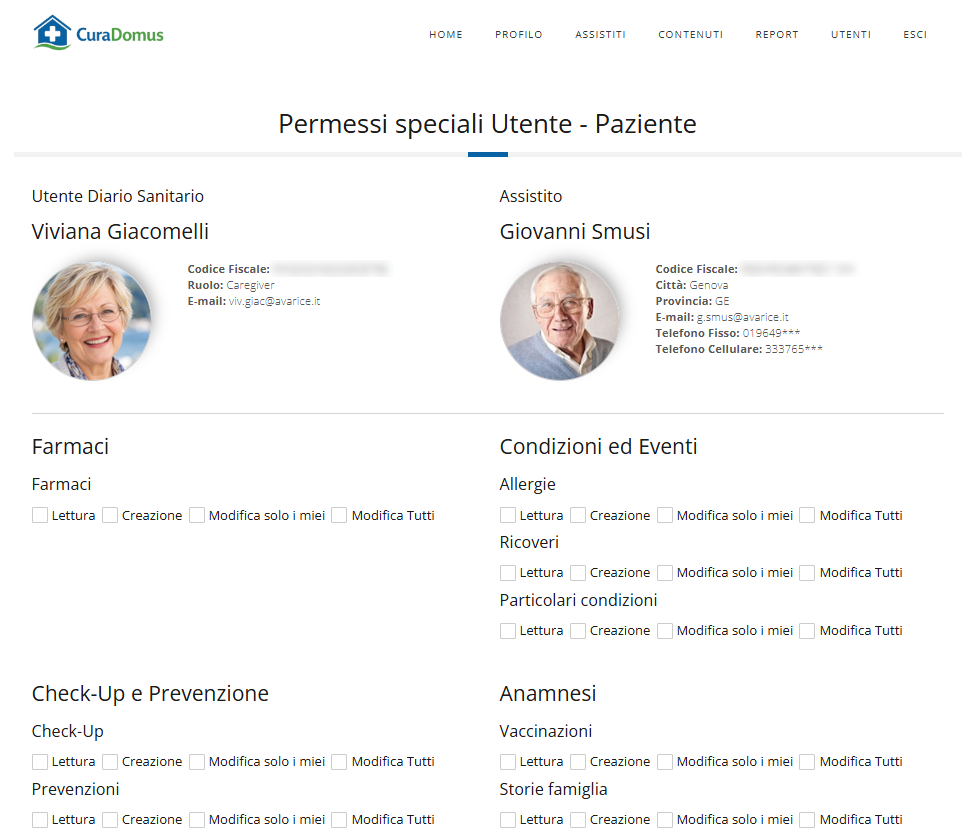
Within this boundary each user has the permissions that fit their role. For every area of the diary, from medication to medical history, you decide whether they can only view, whether they can add new entries and whether they can edit only their own or all of them.
Activity always monitored
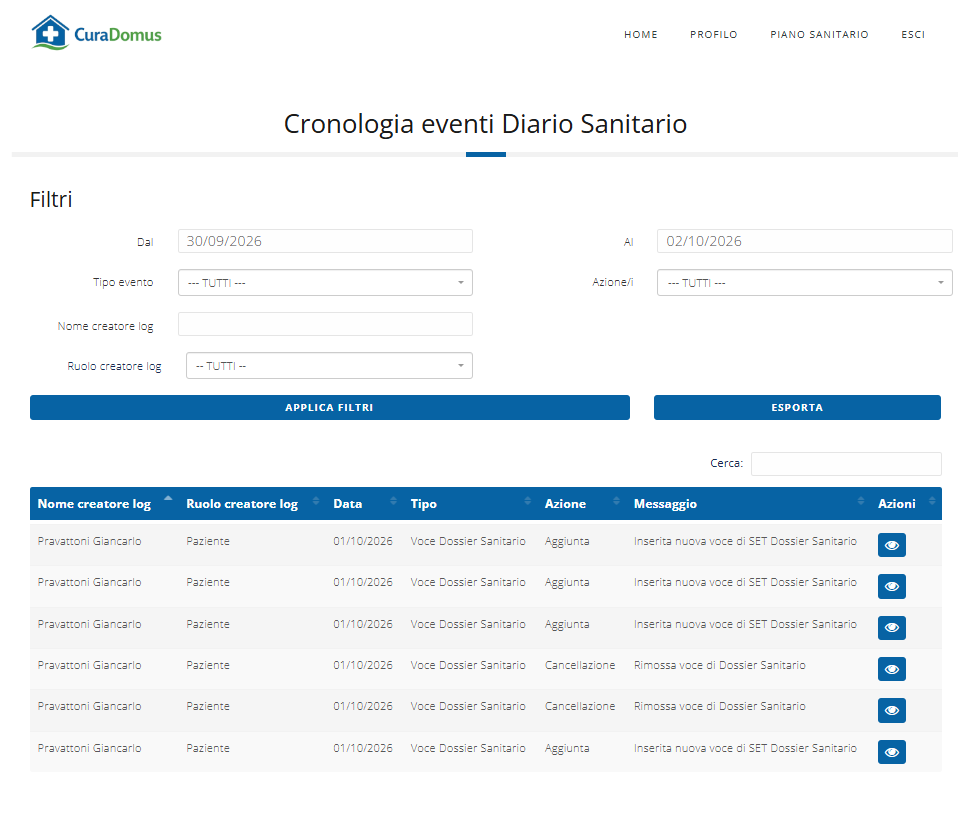
Everything that happens on the platform is logged. Entries, changes and deletions flow into the event history, with author, role and date: it can be filtered by period, event type or person, and exported whenever a check is needed.
What the platform guarantees
Protected access
Secure authentication and a profile for every role: everyone reaches only the functions and the people in their care.
Health data kept apart
Health data is kept separate from other personal data and stored securely.
Many organisations, separate rules
Different organisations and territories work on the same platform, each with its own users and permissions.
GDPR compliance
Consent, sharing and data subject rights handled in line with the GDPR, with the activity history supporting audits.
Want to see it in action?
We will arrange a demo based on your processes and look together at how to integrate it with the systems you already use.